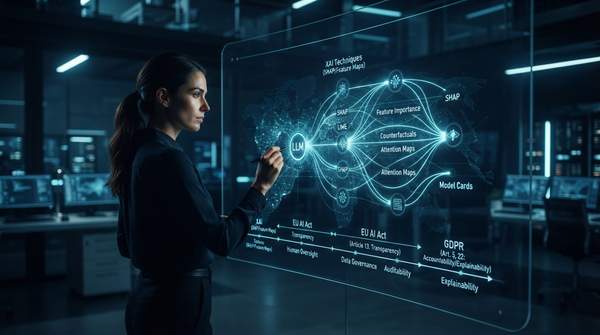
Explainable AI (XAI) is becoming a practical necessity rather than an optional feature for organizations deploying large language models in the EU. The upcoming EU AI Act raises transparency requirements for AI systems starting in 2026, while the GDPR already mandates transparency in automated decisions — and different categories of XAI techniques, from saliency maps to post-hoc explanations and prompt-based reasoning, address different parts of these obligations. This article maps the major XAI technique families to the specific regulatory principles they help demonstrate, giving compliance officers and AI architects a selection framework rather than a general overview.
The Imperative for Explainable AI in LLM Regulation
LLMs pose a distinctive compliance problem: they are "black box" systems whose decision process is not initially clear, which sits awkwardly with laws that demand justification of outputs. Academic work on operationalizing XAI for the AI Act, including a study published on the arXiv repository on the bidirectional relationship between XAI and regulation, argues that XAI — if designed correctly — could play a crucial role in fulfilling the obligations of deployers and providers of AI systems, while cautioning that XAI alone cannot satisfy all AI Act duties.
The practical pressure runs in both directions. Providers and deployers need transparency mechanisms to meet compliance obligations, and the same research frames this as a bidirectional relationship in which XAI practitioners can shape how legal requirements translate into stakeholder-centered implementations. In an interview with the analytics consultancy Statworx, law professor Elena Dubovitskaya argued that the AI Act will increase transparency requirements from 2026, that existing regulations such as the GDPR already demand explainable AI predictions, and that companies adapting early can secure competitive advantages. For LLM teams, the implication is concrete: interpretability work needs to be planned as part of deployment, not retrofitted after an audit fails.
Key Regulatory Drivers: EU AI Act and GDPR
Two bodies of EU law anchor the mandate. First, the AI Act: according to Dubovitskaya, it sets transparency requirements for AI systems and comes into effect in 2026, and it operates on a risk-based approach with distinct roles for providers and deployers, as outlined in a Dutch accounting journal analysis of XAI in EU AI Act compliance audits by Vincent Damen and colleagues. Academic assessment of high-risk AI systems under the AI Act, from a 2025 arXiv paper on translating legal requirements into technical verification, emphasizes that the GDPR is relevant not as an extension of the AI Act but because it provides mature, widely operationalized mechanisms — risk-based assessment, documentation practices, and accountability procedures — that directly inform how AI Act obligations are interpreted and verified in practice.
Second, black box models do not get a grace period until the AI Act applies. Dubovitskaya points out that the GDPR already mandates transparency in automated decisions, and that sector rules add further duties: consumers can demand clear and understandable explanations, including the logic of automated creditworthiness assessments, under the Consumer Credit Directive. She also notes that the new Product Liability Directive, effective December 2024, plays a role, and that an AI Liability Directive is expected to introduce clear liability rules and rights to the disclosure of evidence in cases of damage. A frequently discussed element of this landscape is the GDPR "right to explanation," which post-hoc explanation techniques are often cited as supporting.